Edge Devices Under Fire: Citrix, SonicWall, AhsayCBS Exploited
Citrix NetScaler RCE CVE-2026-107406 needs patching now, SonicWall SMA1000 CVE-2026-102255 is actively exploited, and AhsayCBS flaws are dropping webshells.
Citrix NetScaler RCE and five new CISA KEV adds
Citrix urges immediate patching of critical NetScaler RCE CVE-2026-107406 while CISA added five older flaws to KEV, including a perfect-10 ProFTPD bug.
Citrix NetScaler RCE and Five New CISA KEV Adds
Citrix urges immediate patching of a critical NetScaler ADC and Gateway RCE while CISA adds five old but actively exploited flaws, including a ProFTPD CVSS 10.
Atlassian CVE-2026-21589 Exploited Hours After PoC
Attackers are hitting Atlassian CVE-2026-21589 within hours of public PoC release, while JetBrains TeamCity and PAN-OS KEV flaws stay hot. Patch now.
Atlassian CVE-2026-21589 Under Active Exploitation
Attackers are exploiting critical Atlassian flaw CVE-2026-21589 after a public PoC, hitting Jira and Confluence with unauthenticated file access. Patch now.
Citrix NetScaler CVE-2026-88779 Exploited After Patch
CISA added Citrix NetScaler CVE-2026-88779 to the KEV catalog on October 4 as attackers crash appliances, including some patched days earlier.
Citrix NetScaler SAML Zero-Day CVE-2026-88779 Added to KEV
CISA added actively exploited Citrix NetScaler flaw CVE-2026-88779 to KEV on October 4, with attacks hitting appliances patched days earlier. Patch now.
NetScaler RCE zero-day exploited, Zammad flaws added to KEV
A Citrix NetScaler RCE zero-day is under active exploitation and CISA added two critical Zammad vulnerabilities to the KEV catalog on October 2.
FortiMail Zero-Day CVE-2026-104286 Actively Exploited
CISA added FortiMail path traversal CVE-2026-104286 and two Zammad flaws to KEV this week, with the FortiMail zero-day under active exploitation now.
NetScaler Zero-Days Hit Government and Finance Orgs
Suspected state-sponsored actors exploited Citrix NetScaler zero-days CVE-2026-88771 and CVE-2026-88772 for weeks against government and finance targets.
NetScaler Zero-Days Hit Government and Finance Orgs
Citrix NetScaler zero-days CVE-2026-88771 and CVE-2026-88772 were exploited against government and finance orgs for weeks, with one now CISA KEV listed.
NetScaler Zero-Days Hit Government and Finance Orgs
NetScaler zero-days CVE-2026-88771 and CVE-2026-88772 have been exploited since early September against government and finance orgs. Plus one new Apple KEV add.
CISA Adds SharePoint, WSO2, Adobe Commerce to KEV
CISA added five actively exploited flaws to the KEV catalog on September 24 and 25, including SharePoint CVE-2026-65660 and a WSO2 bug rated CVSS 10.
CISA Adds SharePoint and Adobe Commerce Flaws to KEV
CISA added Microsoft SharePoint CVE-2026-65660 and four more actively exploited flaws to KEV on September 25, including a maxed-out WSO2 path traversal.
Check Point VPN Flaws Added to CISA KEV, Now Exploited
CISA added two Check Point flaws, CVE-2026-85102 and CVE-2026-93616, plus Arista and F5 bugs to KEV on Sept 22, and attackers are already exploiting them.
CISA adds F5 BIG-IP APM and Check Point zero-days to KEV
CISA added exploited F5 BIG-IP APM, Check Point, and Arista VeloCloud zero-days to the KEV catalog on September 22, all with critical CVSS scores. Patch now.
CISA orders agencies to patch Zyxel CVE-2026-7273 by Thursday
CISA added Zyxel GS1900 switch flaw CVE-2026-7273 to KEV after Chinese hackers compromised nearly 1,000 switches for data theft. Patch by Thursday.
Exploited Linux Kernel Bugs and September Windows Patch Fallout
CISA warns of three actively exploited Linux kernel vulnerabilities while September Windows updates break File History backups. Here is what to patch first.
CISA Adds Three Linux Kernel Flaws to KEV Catalog
CISA added three actively exploited Linux Kernel vulnerabilities to the KEV catalog on September 18, including CVE-2026-53266 with a CVSS of 8.8. Patch now.
Cisco ISE Zero-Day Exploited, Plus KEV Movers to Patch Now
Cisco warns of a maximum severity Identity Services Engine zero-day under active attack, while GitLab, SonicWall, and cPanel flaws stay hot on CISA KEV.
Cisco ISE zero-day CVE-2026-76460 added to CISA KEV
Cisco ISE flaw CVE-2026-76460 (CVSS 10) is being exploited unauthenticated and is now on the CISA KEV list. Google Pixel and Acronis Backup were added too.
Cisco ISE CVE-2026-76460 and Pixel Zero-Day Hit CISA KEV
CISA added a CVSS 10 Cisco Identity Services Engine flaw, an exploited Google Pixel zero-day, and an Acronis Backup bug to the KEV catalog on September 16.
Cisco Secure Email Gateway Zero-Day CVE-2026-76461 Hits KEV
Cisco patched an actively exploited Secure Email Gateway SQL injection (CVE-2026-76461, CVSS 9.8), now on CISA KEV, that lets attackers run commands as root.
Cisco Secure Email Gateway added to CISA KEV
CISA added Cisco Secure Email Gateway SQL injection CVE-2026-76461 to KEV on Sept 14, while ScreenConnect and JFrog Artifactory flaws see active exploitation.
ScreenConnect worm-like attacks and September Windows patch fallout
ConnectWise patched a ScreenConnect flaw already exploited in worm-like attacks, while September Windows updates broke audio and RDS. Here is what to do first.
GitLab CVE-2026-85706 and ScreenConnect CVE-2026-84869 Hit KEV
CISA added a max severity GitLab path traversal flaw and a 9.9 ScreenConnect bug to KEV on September 11, with GitLab exploited one day after disclosure.
MikroTik RouterOS CVEs Added to CISA KEV, Cisco FMC Exploited
CISA added two actively exploited MikroTik RouterOS flaws to KEV on Sept 10, while Cisco FMC CVE-2026-20079 draws ransomware and state-sponsored attacks.
Cisco FMC CVE-2026-20079 Now Actively Exploited
CISA added a maximum severity Cisco Firewall Management Center authentication bypass to KEV, with ransomware and state-sponsored actors already exploiting it.
September 2026 Patch Tuesday: 974 CVEs and Two Zero-Days
Microsoft shipped a record 974 CVEs with two exploited zero-days, and CISA added four KEV entries including a Windows and N-able N-central bug. Patch now.
September Patch Tuesday breaks 974-CVE record, two zero-days
Microsoft shipped a record 974 fixes with two exploited zero-days, CISA added four KEV entries, and Google patched its seventh Chrome zero-day of 2026.
September 2026 Patch Tuesday: Microsoft Fixes 974, Two Zero-Days
September 2026 Patch Tuesday: Microsoft fixes 974 vulnerabilities, two exploited zero-days among them; Adobe patches a Magento zero-day used to backdoor sites.
CISA adds ownCloud CVE-2023-49105 to KEV catalog
CISA added ownCloud CVE-2023-49105, a Linux kernel flaw, and JFrog Artifactory to the KEV catalog on 2026-08-27, plus fresh Citrix NetScaler exploitation.
Citrix NetScaler CVE-2026-8452 Exploited, Nine New KEV Adds
Citrix NetScaler CVE-2026-8452 is now exploited in the wild and on the CISA KEV list, alongside nine new KEV additions including an ownCloud auth bypass.
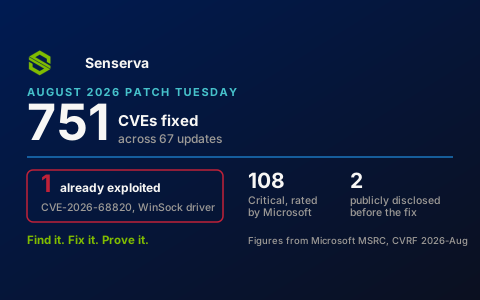
August 2026 Patch Tuesday: 751 Fixes, One Exploited
Microsoft fixed 751 CVEs across 67 updates in August 2026, 108 rated Critical, and one is already being exploited. What to patch first, and why.

Adobe ColdFusion CVE-2026-48282 tops KEV movers with EPSS 0.99
Adobe ColdFusion path traversal CVE-2026-48282, CVSS 10 and CISA KEV listed, has EPSS 0.99. Plus SharePoint, Exchange, and a Zimbra campaign to check.

SharePoint CVE-2026-50522 in CISA KEV, Patch Now
Microsoft SharePoint RCE CVE-2026-50522 (CVSS 9.8) is on the CISA KEV list alongside Adobe ColdFusion CVE-2026-48282 and two Exchange flaws. Patch these first.

Russian Hackers Exploit Zimbra Zero-Day, ColdFusion Hits KEV
Russian actors are exploiting an unpatched Zimbra zero-day against US and Ukraine targets while Adobe ColdFusion CVE-2026-48282 sits on CISA KEV at CVSS 10.

Check Point SmartConsole Zero-Day CVE-2026-16232 Exploited
CISA added Check Point SmartConsole flaw CVE-2026-16232 (CVSS 9.1) to KEV after in-the-wild exploitation, alongside a SharePoint deserialization bug.

WordPress wp2shell CVEs added to CISA KEV as attacks spread
CISA added two WordPress Core flaws (CVE-2026-63030, CVE-2026-60137) to KEV on July 21 as wp2shell attacks install webshells.